
A UK-based accountancy firm was targeted by a severe cyberattack attributed to LockBit ransomware (suspected version 5.0). The breach encrypted the organisation’s core storage infrastructure, rendering all live production data and critical proprietary files inaccessible.
Executive Summary: Successful Data Recovery by SOS Ransomware
- Client sector: Accountancy & Financial Services Firm
- Identified threat: LockBit Ransomware
- Estimated ransom demand: Undisclosed / Unknown
- Hardware scope covered: Production IBM Storwize V3700 SAN (12 TB) & Backup Netgear NAS (12 TB)
- RAID architecture: SAN configured in RAID 50 (2 × RAID 5 arrays of eight 900 GB drives striped in RAID 0 + 1 Hot Spare drive)
- File systems: NTFS (SAN) / Btrfs (NAS)
- Total raw data recovered and delivered: 5.8 TB out of 12 TB (NAS) + supplementary data (SAN)
- Priority data recovery rate: Partition 1 recovered at 95% (~3 TB) | Partition 2 recovered at 98% (~1 TB)
- Data recovery specialist: Recoveo / SOS Ransomware
Infrastructure Impacted by the Attack
The affected infrastructure comprised two mission-critical storage assets:
- Un SAN IBM Storwize V3700 (12 To) configuré en RAID 50 (deux grappes RAID 5 de 8 disques de 900 Go combinées en RAID 0, accompagnées d’un 17ᵉ disque de secours Hot Spare) sous système de fichiers NTFS.
- Un NAS Netgear (12 To) (avec File System en BTRFS)
Initial Technical Forensic Analysis
Upon reception at the Recoveo laboratory, engineering teams executed a strict, forensically sound diagnostic protocol:
- Physical Drive Cloning: To preserve the absolute integrity of original evidence, every hard drive from both the NAS and SAN was sector-by-sector cloned onto secure target media.
- RAID 50 Array Rebuilding: Engineers successfully reassembled the SAN’s RAID 50 array to reveal the initial file system tree. By analyzing a specific hard drive from the SAN, Virtual Hard Disk (VHDX) images were extracted, containing the client’s critical proprietary files.
The Strategic Importance of Multi-Source Data Recovery
Initial test results prior to the full NAS deep scan confirmed high recovery rates for primary business files.
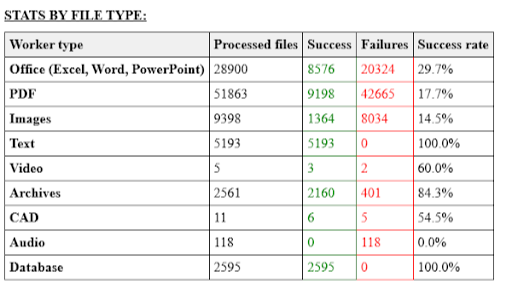
File Extraction Ahead of Deep Scan
NAS-Side Extraction (Btrfs): Deep forensic analysis of the Btrfs file system on the NAS unearthed historical data snapshots, securing approximately 4 TB of historical files.
Source Complementarity: By cross-referencing file fragments between the SAN and NAS, engineers reconstructed missing data blocks. For instance, metadata extracted from the NAS enabled the full reconstruction of corrupted proprietary files on the SAN.
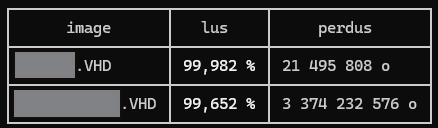
Recovered Proprietary Business Files
Victim of a LockBit Ransomware Attack? Are Your SAN or NAS Storage Systems Inaccessible?
